
Validating tool input and tool results
Every tool call has two trust boundaries — the arguments in and the results out.
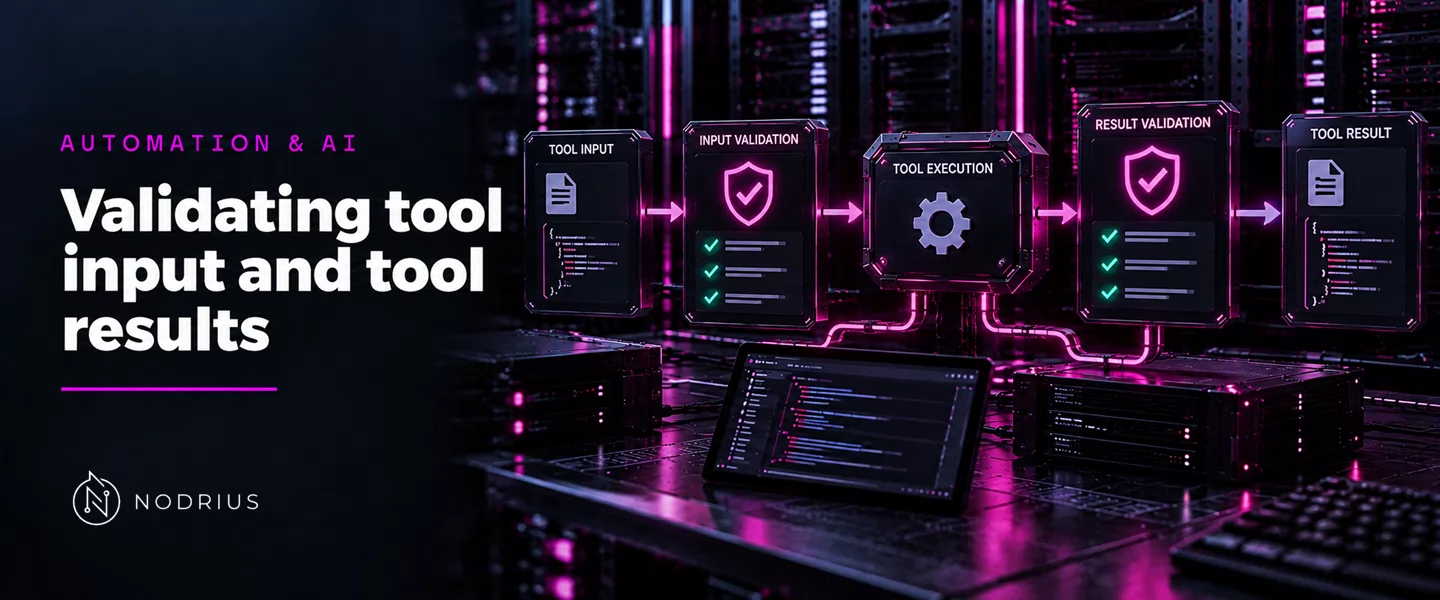
A tool call crosses two trust boundaries. In, a model proposes arguments for a function it cannot run: a request, not a fact. Out, the tool returns a result that will be shown to a user, fed back to the model, or handed on. A schema declares what each side should look like; validation is the runtime gate that compares the payload against that declaration before anything acts on it — and the Model Context Protocol’s guidance treats the two as separate obligations.
The two boundaries of a tool call
When a model calls a tool, it “returns a structured call that your application executes”
(anthropic-tool-use.txt 47): the model picks the arguments, your code runs the operation, and a second
request returns the outcome so the model can continue. The input is that argument object — values
chosen from a tool description, with no guarantee the model had the information to choose them correctly.
The result is the tool’s return value: text, structured content, an error, or a link to further data.
What a schema does — and what it does not do
JSON Schema is the declaration language both sides share. It “defines the media type
application/schema+json, a JSON-based format for describing the structure of JSON data” and “asserts
what a JSON document must look like” (json-schema-core.txt 48–50); the document checked is the
“instance” (line 408). What validation means is explicit: “Validation keywords in a schema impose
requirements for successful validation of an instance. These keywords are all assertions without any
annotation behavior.” (json-schema-validation.txt 325–326). Passing means the instance matched the
schema.
Two defaults weaken that. A schema is permissive unless written otherwise: “By default, leaving out
properties is valid.” and “By default, providing additional properties is valid:”
(json-schema-understanding-object.txt 134, 150), so a schema that lists fields but requires none of
them accepts almost any object. And format is an annotation, not an assertion: format
checking is “disabled by default” (json-schema-validation.txt 611–618), with semantic validation in the
application “the recommended best practice” (lines 639–640). Shape conformance is a floor, never the whole
test.
The input gate: validate the arguments before you execute
The model is not a trusted caller. When a required parameter is missing it may not stop: it “might also
infer a reasonable value” (anthropic-tool-use.txt 130) and “might guess values you didn’t supply” (line
131), behaviour the page calls “not guaranteed” for ambiguous prompts or weaker models (line 140). A
definition can ask the provider to constrain generation — strict: true ensures “Claude’s tool calls
always match your schema exactly” (line 127) — but that is a property of the model’s output, not a check in
the executor. The gate that matters runs after the arguments arrive: validate them against the schema, then
apply the semantic checks a schema cannot express (ranges, allowed paths, tenant, whether the action was
ever permitted). OWASP puts it as “Treat the model as any other user, adopting a zero-trust approach, and
apply proper input validation” (owasp-llm-top10-2025.txt 907–908) to backend functions.
The result gate: validate and sanitise before you trust it
A result is not automatically a fact. Where a server publishes an output schema, the protocol makes both
sides responsible: servers “MUST provide structured results that conform to this schema” and clients
“SHOULD validate structured results against this schema” (mcp-tools-new.txt 264–267). Where no schema
exists, the result still has a shape to check before it is parsed. Errors need their own path: MCP
separates protocol errors (unknown tool, invalid arguments, server errors) from execution errors reported
“with isError: true” (lines 327–335), so a failed lookup is never read as a valid payload. And the result
becomes input somewhere else, which makes this a security boundary: OWASP’s Improper Output Handling
(LLM05) is “insufficient validation, sanitization, and handling of the outputs generated by large language
models before they are passed downstream to other components and systems” (owasp-llm-top10-2025.txt
863–865), with consequences named as “XSS and CSRF in web browsers as well as SSRF, privilege escalation,
or remote code execution on backend systems” (lines 870–872). Well-formed is table stakes; safe to act on
is the harder half.
Where validation stops
Validation checks conformance; it does not make content safe. Sanitising and encoding for the destination
are separate controls: “Follow the OWASP ASVS (Application Security Verification Standard) guidelines to
ensure effective input validation and sanitization.” (owasp-llm-top10-2025.txt 910–911) and “Encode
model output back to users to mitigate undesired code execution by JavaScript or Markdown.” (lines
913–914). Metadata is untrusted too: “clients MUST consider tool annotations to be untrusted unless they
come from trusted servers” (mcp-tools-new.txt 184–185). Neighbouring sheets split this surface
deliberately: the schema-and-arguments sheet owns the schema and argument validation, and
this sheet owns the two runtime gates around a call. Validation
answers “does this match the contract?”, not “should this happen?”.
Level and prerequisites. L4 — operations-and-risk: the reader must treat every value a model or a remote server produces as untrusted and place an explicit gate on both sides of a call. Prerequisites: the L3 sheets on tool/function calling (schema, call and result) and the L1/L2 sheets on model behaviour, context and structured output.
Where to go next
- Automation & AI — the macro-area this sheet belongs to.
- Operations and risk — the node this sheet sits in.
References
- IETF JSON Schema drafts — Core and Validation — what a schema is, what validation asserts, and why
formatis an annotation while permissive defaults leave objects open. - JSON Schema — Understanding JSON Schema: object — the “valid by default” behaviour of omitted and additional object properties.
- Anthropic — Tool use with Claude — the round trip, strict tool use, and the model guessing missing arguments.
- Model Context Protocol — Tools — the two-sided validation obligations, output-schema validation, and the protocol-versus-execution error split.
- OWASP — Top 10 for LLM Applications (2025) — LLM05 Improper Output Handling and the zero-trust input stance.