
Gap assessment and the treatment plan: from a finding to an owner and a date
A gap becomes a plan only when a finding gets an owner, a date and a decision.
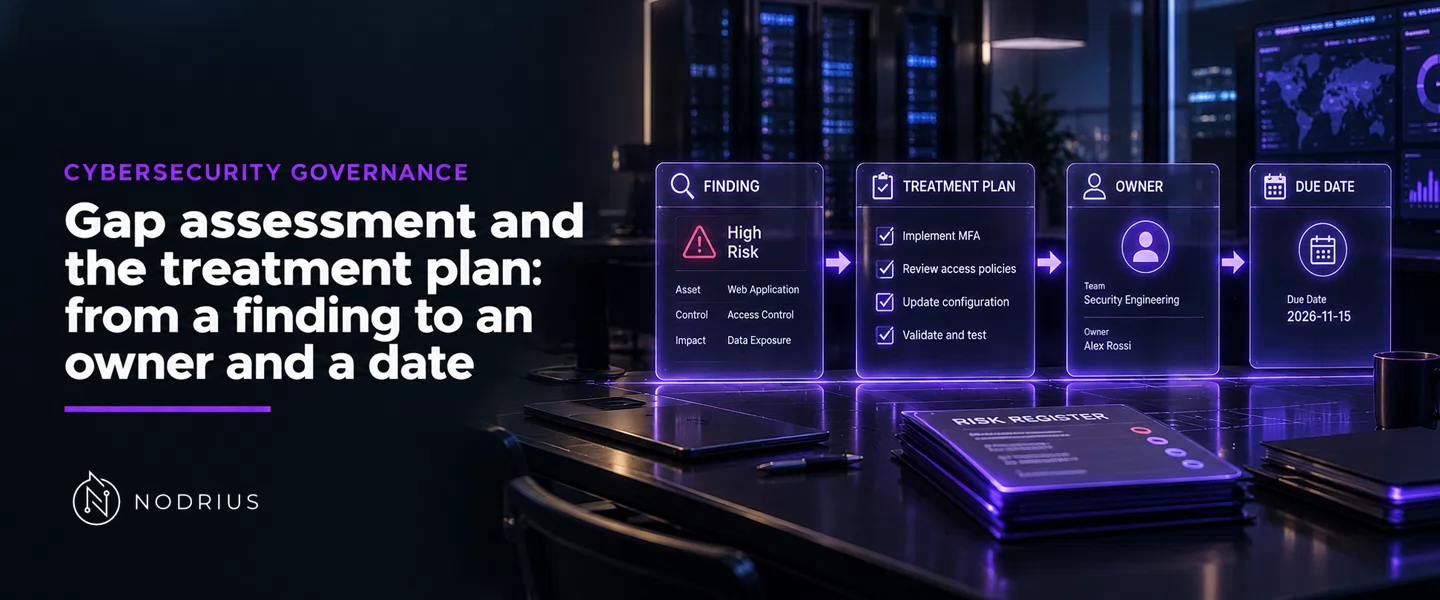
A gap assessment produces one usable output: a plan. The comparison and the findings only say where the organisation is behind; the plan is where “we are not where we said we would be” becomes work with owners and dates. CSF 2.0 directs the organisation to compare a Current Profile with a Target Profile and turn the difference into an action plan; the NIST control set gives that plan a named record — the plan of action and milestones — and a process that keeps it alive.
A gap is a difference between two profiles
NIST CSF 2.0 states the step plainly: “Analyze the gaps between the Current and Target Profiles, and create an action plan” (line 405), and it says what the analysis has to yield — “a prioritized action plan (e.g., risk register, risk detail report, Plan of Action and Milestones [POA&M]) to address those gaps” (lines 406–408). Step 5 then runs the plan and updates the profile, with the reminder that “An action plan may have an overall deadline or be ongoing” (lines 410–412). The Core is a set of outcomes and “not a checklist of actions to perform” (lines 243–245), so a gap is measured against outcomes, not against a task list; and the same Core is offered to “determine gaps, and assess progress toward addressing those gaps” (lines 186–188). The comparison itself, and the Tiers, belong to the sibling sheet on the CSF profiles; this sheet begins where the comparison ends.
From a gap to a plan of action and milestones
A gap becomes treatment when it enters a named record. CA-5 requires the organisation to “Develop a plan of action and milestones for the system to document the planned remediation actions of the organization to correct weaknesses or deficiencies noted during the assessment of the controls” (lines 6636–6639), and to update it “based on the findings from control assessments, independent audits or reviews, and continuous monitoring activities” (lines 6641–6643). PM-4 lifts the same record to the organisation: plans must “Are developed and maintained” and “Are reported in accordance with established reporting requirements” (lines 13748–13758). It adds the review that makes a plan a governance document — plans are checked “for consistency with the organizational risk management strategy and organization-wide priorities for risk response actions” (lines 13760–13761). That clause separates a treatment plan from a local to-do list: a row answers to the risk strategy, not only to its author.
Findings become priorities
SP 800-53A fixes the vocabulary of a finding. Each determination statement produces one of two outcomes — “satisfied (S); or” / “other than satisfied (O)” (lines 2166–2167) — and only the second asks for work; it also covers the assessor who “was unable to obtain sufficient information” (lines 2176–2178). Priority is a separate, deliberate act: “organizations may choose to define subcategories of findings indicating the severity and/or criticality of the weaknesses or deficiencies discovered”, and “Defining such subcategories can help to establish priorities for needed risk mitigation actions” (lines 2178–2183). Severity is thus the organisation’s choice, not the assessor’s to hand over. The finding and the plan travel as one package: the authorisation package “consists of the security plan, privacy plan, security assessment report, privacy assessment report, and plan of action and milestones (POA&M)” (lines 2191–2192).
The plan is only as current as the monitoring that feeds it
Treating a gap is not a one-off. SP 800-37r2 Task M-4 requires the organisation to “Update plans, assessment reports, and plans of action and milestones based on the results of the continuous monitoring process” (lines 5321–5322). Its discussion gives a finding two legitimate destinations: where “the risk response is acceptance, the findings remain documented in the security and privacy assessment reports and are monitored for changes to risk factors”, and where “the risk response is mitigation, the planned mitigation actions are included in and tracked using the plans of action and milestones” (lines 5304–5307). Accepting a gap and treating it are both decisions; only silence is a failure.
What a plan cannot do
Three limits bound the artefact. First, a plan is a commitment, not a closure: a row marked complete records that work was undertaken, and evidence that the control now works is a different artefact — the verification of the fix belongs to the L3 sheet on remediation verification and residual risk. Second, a gap assessment measures against the framework the organisation chose, so it cannot show more than that framework’s outcomes contain; alignment with the Core is not evidence of security. Third, a POA&M row with no owner, no date and no acceptance decision is a record of intention, not of treatment.
what assessment found          what the organisation does with it
"satisfied (S)"             →  nothing to treat
"other than satisfied (O)"  →  a severity subcategory                 (SP 800-53A §3.3)
                            →  a POA&M row: action, owner, date       (CA-5)
                            →  or a recorded decision to accept it    (SP 800-37r2 M-4)
                            →  monitoring results feed the next update (Task M-4)
Level and prerequisites
L4 — assurance: the sheet turns a framework’s comparison into a governed artefact, and asks how a finding acquires a priority, owner and date, and what the artefact cannot prove. It assumes the L1 vocabulary (control, assessment, evidence), the L2 risk and exception register and control objectives and verification criteria, and the L3 sheet that owns the verification of the fix and the residual risk. It does not re-teach the comparison of profiles or the statement of applicability.
Where to go next
- Knowledge — the Knowledge register.
- Cybersecurity Governance — the macro-area.
- Assurance — the node this sheet sits in.
References
- NIST CSF 2.0 (NIST CSWP 29) — the Current and Target Profiles, the gap-analysis step and the action plan, and the outcome-not-checklist caution.
- NIST SP 800-53 Rev. 5 — CA-5 and PM-4, the plan of action and milestones and the organisation-level process that maintains and reports it.
- NIST SP 800-53A Rev. 5 — the two findings, the severity subcategories, and the authorisation package that carries the report and the plan together.
- NIST SP 800-37 Rev. 2 — Task M-4, the update of plans, assessment reports and plans of action and milestones from continuous monitoring.