
Exceptions, approvals and compensating controls: the life of an accepted deviation
Who may approve a deviation, what compensates for it, and what ends it at expiry.
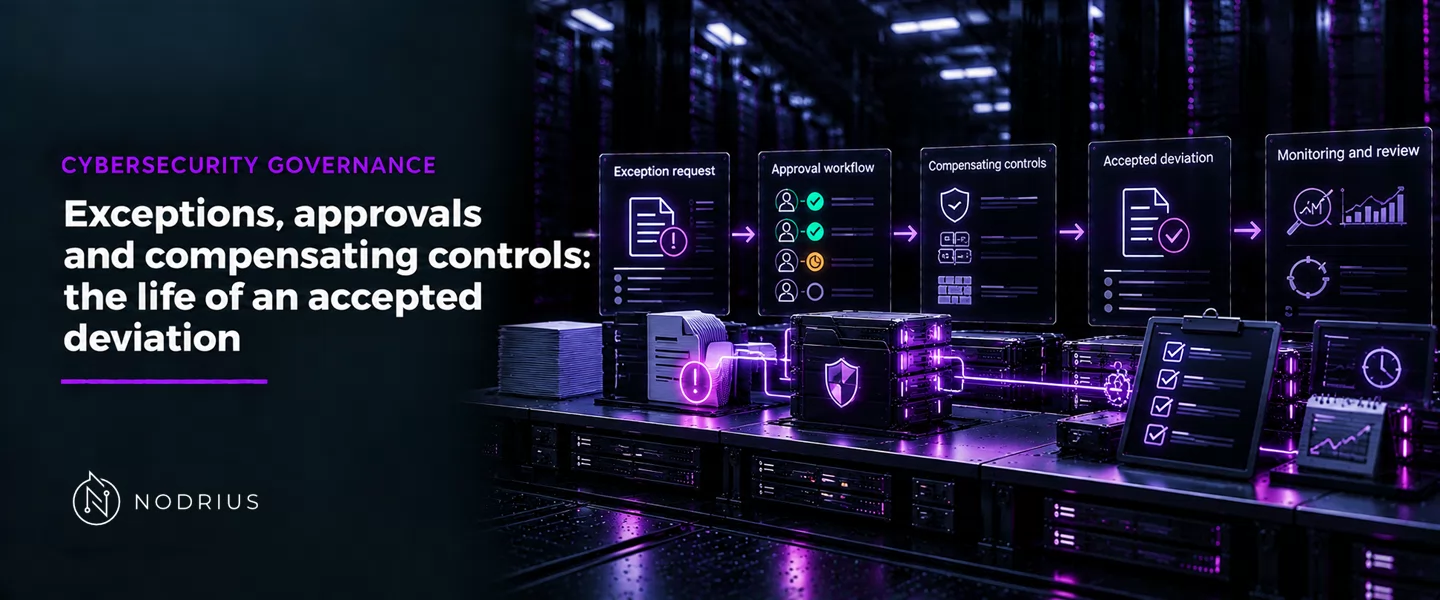
Three things have to be kept apart before a deviation can be governed. An exception is a recorded, time-bound, owned permission to depart from a baseline; a risk acceptance is a decision taken by someone with the authority to live with what remains; a compensating control is the measure that must give equivalent protection while the departure lasts. The life of an accepted deviation links an equivalence test, an approval that cannot be delegated, a record people can find, and an end somebody owns.
Three objects, three questions
One decision usually produces all three.
- The exception answers what was allowed, by whom, and until when.
- The acceptance answers who decided to bear the residual risk.
- The compensating control answers what stands in for the missing control.
An exception with no acceptance behind it is an undocumented habit; an acceptance with no compensating measure is a decision nobody implemented.
What makes a control compensating
SP 800-18r1 carries the definition used here: compensating security controls are “the management, operational, or technical controls employed by an agency in lieu of prescribed controls in the low, moderate, or high security control baselines, which provide equivalent or comparable protection for an information system” (§2.5.2, lines 868–871). The load-bearing word is equivalent: the substitute has to be argued to protect as well as what it displaces. SP 800-53A r5 prints the catalogue-side form — controls “employed in lieu of the controls in the baselines described in NIST Special Publication 800-53B” — and attributes it to SP 800-53B (line 43123), a publication absent from this evidence set.
The approval gate
Employment is conditional on three things in SP 800-18r1: the controls are selected from the SP 800-53 catalogue; the organisation gives “a complete and convincing rationale and justification” for how they provide an equivalent security capability or level of protection; and the organisation “assesses and formally accepts the risk” of employing them (lines 871–877). The use itself “must be reviewed, documented in the system security plan, and approved by the authorizing official for the information system” — a sentence that begins on line 877 and resumes on lines 898–899, with a footnote block in between. Scoping decisions need the same approval (§2.5.1, lines 748–750), from the official identified in the plan who accepts “the residual risk associated with the system” (§3.4, lines 1092–1095).
Who may accept
The acceptance does not move downwards: “The explicit acceptance of risk is the responsibility of the authorizing official and cannot be delegated to other officials within the organization” (SP 800-37r2, lines 4942–4943). The decision carries the authorization’s “terms and conditions” and its termination date “or time-driven authorization frequency” (lines 4960–4962); that date “indicates when the authorization expires” (lines 4994–4995). Under an ongoing authorization the same official keeps accepting the risk and, where it is no longer acceptable, “requires further risk response or a full denial of the authorization” (lines 5012–5021).
Where the deviation is recorded
CSF 2.0 names the duty at ID.RA-07: changes and exceptions are managed, assessed for risk impact, recorded and tracked (lines 905–906). The catalogue names an approved deviation once: CM-8(6) requires organisations to “include assessed component configurations and any approved deviations to current deployed configurations in the system component inventory” (lines 7932–7935). The numbering is worth checking: SP 800-53A r5 prints the same enhancement as CM-08(06) (line 12991), while the SP 800-53r5 summary table shifts the row. The change record is CM-3’s: the decision documented, the records retained (lines 7245, 7254); who approves a change, and on what analysis, is the change-approval sheet’s subject. Where compensation is a stopgap, CA-5 puts the remaining work into a plan of action and milestones (lines 6636–6646).
When the deviation ends
An exception with no end is a permanent baseline change. SP 800-30r1 supplies the sharpest trigger: a risk assessment “conducted to inform a Tier 3 decision on the use of a compensating security control for an information system may be relevant only until the next release of the information technology product providing the required security capability” (lines 1749–1751). The evidence behind the substitution expires with the thing it was used against, and the same publication dates a mission change “for a specific time frame (e.g., … until a compensating control is replaced)” (lines 650–652). SP 800-39 puts compensation among the ordinary responses to risk (lines 1824–1827).
Measuring what remains
NISTIR 8286r1 defines risk tolerance as “the organization or stakeholders’ readiness to bear the remaining risk after responding to or considering the risk” (lines 587–588), and separates actual residual risk from target: actual “should be equal to or less than the target residual risk” (lines 1165–1166). An accepted deviation therefore carries a test, because accepted entries “need to be measured to ensure that they remain within established risk tolerance parameters” (lines 2004–2006); the remaining risk is recorded in the register’s Residual Risk column (lines 1606–1609).
Level and prerequisites
L3 — assessment and control selection. The sheet assumes the L1 vocabulary of risk response and acceptance criteria and the L2 record of what was accepted, and works on the mechanism between them. The content of any compensating measure, and the arithmetic of deadlines, belong elsewhere.
Where to go next
- Knowledge — the index.
- Cybersecurity Governance — the area this sheet belongs to.
- Risk management — this sheet’s node.
Above this material sit the L1 sheets on risk treatment options and on risk appetite and acceptance criteria; the L2 register sheet owns the rows these decisions are written into. All are unpublished and named in prose only.
References
- NIST — SP 800-18 Rev. 1, Guide for Developing Security Plans for Federal Information Systems (February 2006) — https://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-18r1.pdf — the definition of a compensating security control, the three conditions for employing one, the requirement that its use be reviewed, documented in the security plan and approved by the authorizing official, and the identity of that official.
- NIST — SP 800-53 Rev. 5, Security and Privacy Controls for Information Systems and Organizations (September 2020) — https://doi.org/10.6028/NIST.SP.800-53r5 — CM-8(6) (assessed configurations and approved deviations in the component inventory), CM-3 (the record of a configuration-controlled change) and CA-5 (plan of action and milestones).
- NIST — SP 800-53A Rev. 5, Assessing Security and Privacy Controls in Information Systems and Organizations (January 2022) — https://doi.org/10.6028/NIST.SP.800-53Ar5 — the glossary entry for compensating controls and the CM-08(06) numbering that confirms CM-8(6).
- NIST — SP 800-37 Rev. 2, Risk Management Framework for Information Systems and Organizations (December 2018) — https://doi.org/10.6028/NIST.SP.800-37r2 — the non-delegable acceptance of risk by the authorizing official, the terms and conditions and the termination date of an authorization, and the ongoing authorization case.
- NIST — SP 800-30 Rev. 1, Guide for Conducting Risk Assessments (September 2012) — https://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-30r1.pdf — the shelf life of the risk assessment behind a compensating control, and the time-bound mission modification.
- NIST — SP 800-39, Managing Information Security Risk: Organization, Mission, and Information System View (March 2011) — https://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-39.pdf — compensating controls as one of the ordinary responses to risk.
- NIST — NISTIR 8286r1, Integrating Cybersecurity and Enterprise Risk Management (ERM) (December 2025) — https://doi.org/10.6028/NIST.IR.8286r1 — risk tolerance, actual versus target residual risk, the register’s Residual Risk column, and the rule that accepted risks are still measured.
- NIST — The NIST Cybersecurity Framework (CSF) 2.0, NIST CSWP 29 (26 February 2024) — https://doi.org/10.6028/NIST.CSWP.29 — ID.RA-07: changes and exceptions are managed, assessed for risk impact, recorded and tracked — the framework’s own statement of the duty the body opens with, cited in “Where the deviation is recorded”.