
Severity and risk context: why a severity score is not a priority
A severity score describes the vulnerability, not your exposure. Read it in context.
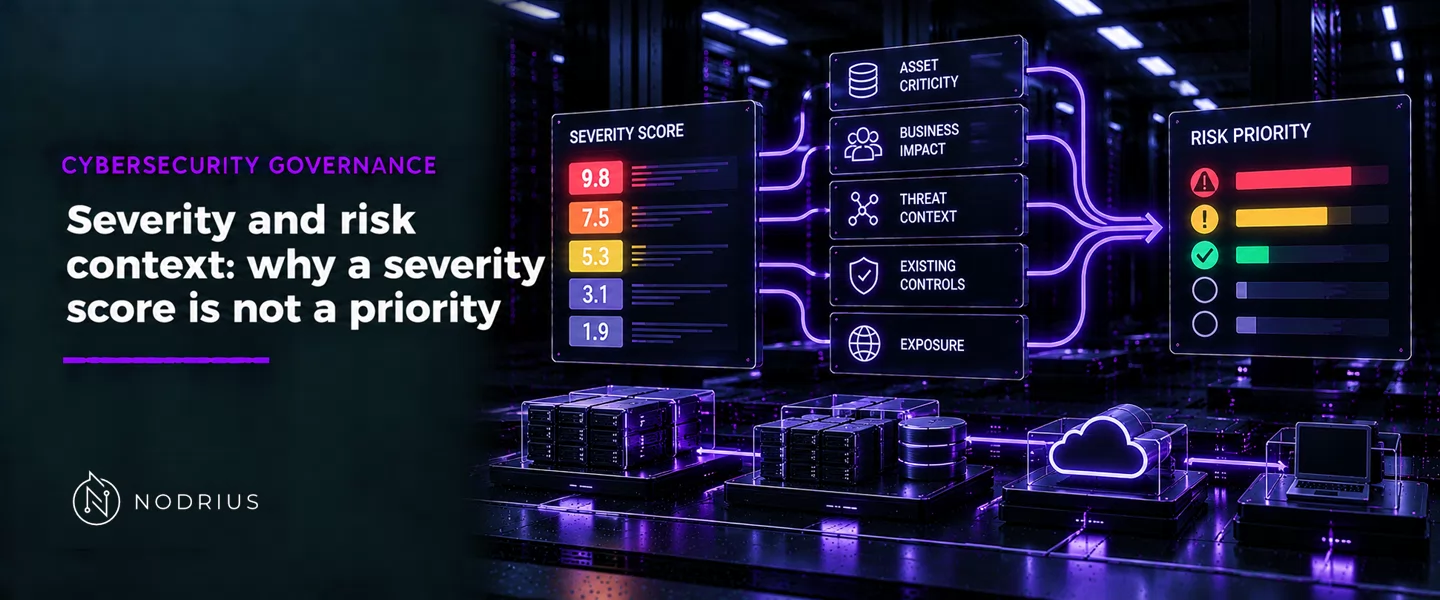
A severity score describes a vulnerability; a priority describes your situation. CVSS, the Common Vulnerability Scoring System, is “an open framework for communicating the characteristics and severity of software vulnerabilities”, and the number most often quoted assumes the reasonable worst case. It answers how bad could this weakness be if nothing else were known — not how much this finding matters here, now, on this asset. The distance between the two is risk context, and the specification itself says where the gap lies.
What CVSS measures: four metric groups
CVSS v4.0 (specification document version 1.2) consists of four metric groups: Base, Threat, Environmental and Supplemental. The Base group holds characteristics “constant over time and across user environments”. Threat holds what changes with time. Environmental holds what is “unique to a user’s environment” — the mitigations that would blunt the attack and “the criticality attributes of the vulnerable system”. Supplemental metrics add context, but no metric in that group “will have any impact on the final calculated CVSS score”. The version boundary is part of reading a score: CVSS v3.1 is built on three groups, Base, Temporal and Environmental. Both specifications print the same five bands (None 0.0; Low 0.1–3.9; Medium 4.0–6.9; High 7.0–8.9; Critical 9.0–10.0), so a band taken from one model and applied to a number from the other is an assumption, not a reading.
The number you are handed is a worst case
The Base Score “assumes the reasonable worst-case impact across different deployed environments”, because “Base metric values are combined with default values that assume the highest severity for Threat and Environmental metrics”. The consumer’s own values enter only if somebody supplies them: “The absence of explicit Threat and/or Environmental metric selections will still result in a complete score using default (“Not Defined”) values”, and the default for exploit maturity “is equivalent to Attacked (A)… by assuming the worst case”. Assessment providers “typically provide only the Base Scores enumerated as CVSS-B”. A published number is therefore an answer to a deliberately pessimistic question.
what is published             what the consumer adds          what the consumer then holds
---------------               ----------------------          ----------------------------
CVSS-B: Base metrics    -->   Threat: exploited in the   -->  a severity for this system,
only, with the worst-         wild? proof-of-concept?         labelled CVSS-BTE, with the
case defaults for the         available tooling?              vector string showing which
metrics nobody supplied  -->  Environmental: mitigations,     metric groups were used
                              asset criticality
                                     |
                                     v
                   the facts a score still cannot carry: exposure, mission,
                   risk tolerance, legal or regulatory duty
What the specification itself puts outside the score
The specification claims no neutrality. “Consumers of CVSS should enrich the Base metrics with Threat and Environmental metric values specific to their use of the vulnerable system to produce a score that provides a more comprehensive input to risk assessment specific to their organization.” Even then it is an input to a process “that also considers factors that are not part of CVSS in order to rank the threats to their technology infrastructure and make informed remediation decisions” — the factors it lists are regulatory requirements, customers affected, monetary losses, life or property threatened and reputational impact, and “These factors are outside the scope of CVSS.” The naming rule follows from that: “the usefulness of a numerical CVSS score is directly proportional to the CVSS metrics leveraged to generate that score”. CVSS-B, CVSS-BT and CVSS-BTE are three different claims.
Severity is a relative reading, and the relative term is yours
NIST SP 800-30 Rev. 1 defines the term rather than a formula: “The severity of a vulnerability is an assessment of the relative importance of mitigating/remediating the vulnerability.” Its conclusion is blunt — “the severity of vulnerabilities, in general, is context-dependent” — and the same finding therefore weighs differently on two systems. That is what the Environmental group is for: it is where mitigations and system importance enter the number. It is also why the bands are a convenience, not a duty: “The use of these qualitative severity ratings is optional, and there is no requirement to include them when publishing CVSS scores.”
The facts a severity cannot carry
The sources stop treating severity as a single number where an action has to be chosen. SP 800-53 Rev. 5’s SI-2 discussion names five risk factors that may vary the period allowed for installing an update: the security category of the system, “the criticality of the update (i.e., severity of the vulnerability related to the discovered flaw)”, “the organizational risk tolerance”, the mission supported by the system, and the threat environment. The reverse case appears in the same publication: a severity threshold is set “in accordance with organizational risk tolerance”. That line is drawn locally, not received.
Inputs to a decision, never the decision
CISA’s BOD 26-04 (10 June 2026, for US federal systems) makes technical impact one of four variables behind the urgency of remediation, and describes it as “similar to the Common Vulnerability Scoring System (CVSS) base score’s concept of ‘severity’”. CISA’s instruction for its Known Exploited Vulnerabilities catalog has the same shape: “Organizations should use the KEV catalog as an input to their vulnerability management prioritization framework.” Which finding goes first, and by when, is a sibling subject; this sheet establishes only what the score is and is not.
Level and prerequisites
L3 — assessment, control selection and process coordination. It assumes the L1 vocabulary of threat, vulnerability, likelihood and impact, and the L2 sheets of this area that fix what an inventory and a criticality analysis contain. Here one input is read and its limits stated; the decision it feeds is a sibling subject.
Where to go next
References
- NIST — Guide for Conducting Risk Assessments (SP 800-30 Rev. 1, September 2012) — no DOI is printed in the converted text used here, so the publication is cited by number — the definition of vulnerability severity as a relative and context-dependent assessment (lines 845–847).
- NIST — Security and Privacy Controls for Information Systems and Organizations (SP 800-53 Rev. 5) — https://doi.org/10.6028/NIST.SP.800-53r5 —
SI-2and its discussion (lines 21740–21766): the period allowed for installing an update varies with five risk factors, of which vulnerability severity is one;SA-15(1)severity thresholds set “in accordance with organizational risk tolerance” (line 18551, lines 18564–18573). - NIST — The NIST Cybersecurity Framework (CSF) 2.0 (NIST CSWP 29) — https://doi.org/10.6028/NIST.CSWP.29 — ID.RA-04 and ID.RA-05: impacts and likelihoods identified and recorded, then used together to inform risk response prioritization (lines 897–901).
- FIRST — Common Vulnerability Scoring System version 4.0: Specification Document (document version 1.2) — https://www.first.org/cvss/v4.0/specification-document — the four metric groups (line 221); the worst-case defaults and the score range (lines 226–231); the Base Score’s worst-case assumption (lines 253–256); the risk-assessment boundary and the factors “outside the scope of CVSS” (lines 267–277); the CVSS-B/BT/BTE nomenclature (lines 355–387); the exploit-maturity default (lines 682–683); the optional qualitative bands (lines 964–981).
- FIRST — Common Vulnerability Scoring System version 3.1: Specification Document — https://www.first.org/cvss/v3-1/specification-document — the three metric groups of the earlier model and the Base Score’s worst-case reading (lines 219–258); the factors a consumer must add and those outside CVSS (lines 259–268); the qualitative severity rating scale, Table 14 (lines 697–718).
- Cybersecurity and Infrastructure Security Agency — BOD 26-04: Prioritizing Security Updates Based on Risk (10 June 2026) — https://www.cisa.gov/news-events/directives/bod-26-04-prioritizing-security-updates-based-risk — the four variables that determine the urgency of remediation (lines 97–101); the SSVC basis (line 170); technical impact likened to the CVSS base score’s concept of severity (line 171).
- Cybersecurity and Infrastructure Security Agency — Known Exploited Vulnerabilities Catalog — https://www.cisa.gov/known-exploited-vulnerabilities-catalog — the catalog used “as an input to their vulnerability management prioritization framework” (line 381).