
NAT and PAT: what translation does, and why it is not a security control
NAT and PAT rewrite a packet header; the filtering is a side effect of that state.
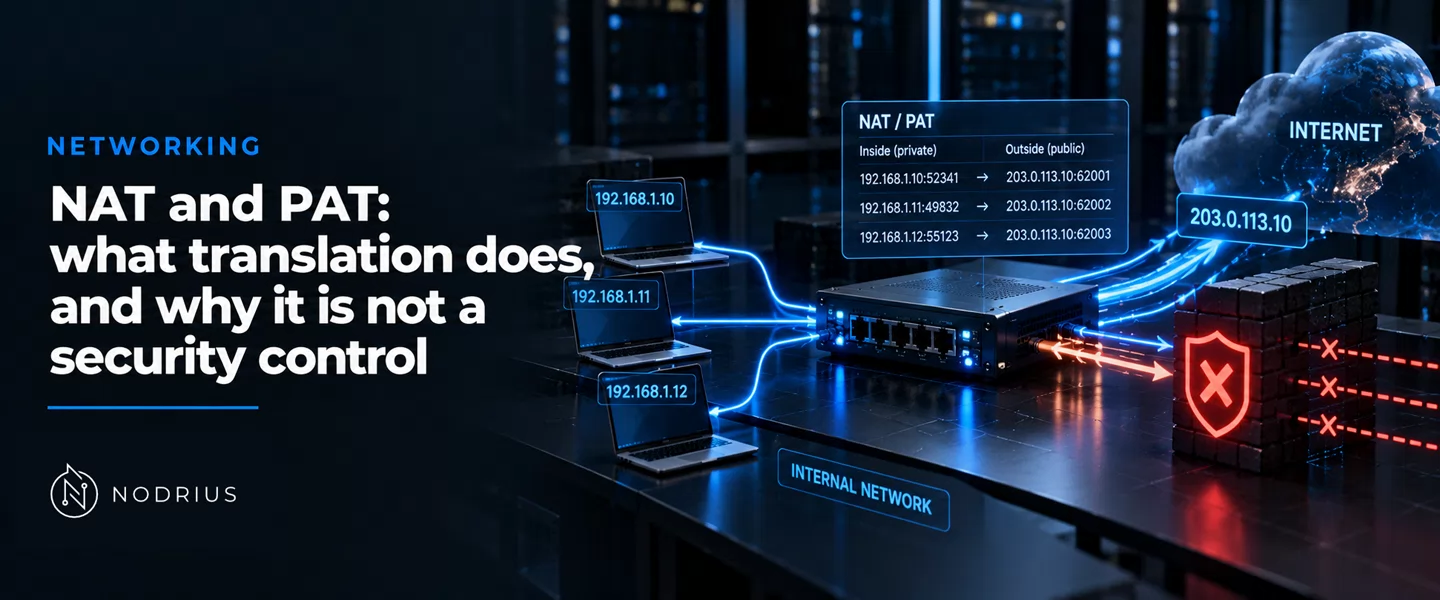
NAT (Network Address Translation) rewrites the IP addresses in a packet header as the packet crosses between two address realms. PAT (Port Address Translation — the IETF’s NAPT) rewrites transport ports as well, so many internal hosts can share a single public address. Both are translation mechanisms, and the filtering people credit them with is a side effect of the state translation needs, not a designed control. The IETF says so without hedging: IPv4 “NAT was not developed as a security mechanism. Despite marketing messages to the contrary, it is not a security mechanism” (RFC 4864).
The problem translation solves
An internal host numbered with a private address has no globally routable address, so its packets cannot return from the Internet. A NAT device sits at the border between the private realm and the public one and maps addresses “from one realm to another” (RFC 2663 §3). RFC 2663 names the private blocks it works with — “10/8, 172.16/12, and 192.168/16” — and Cisco’s configuration guide states the operational version: “Before packets are forwarded onto another network, NAT translates the private (not globally unique) addresses in the internal network into legal addresses.” A NAT can be configured to “advertise to the outside world only one address for the entire network” — that single address is PAT’s whole reason for existing.
What each variant rewrites
- Basic NAT translates the address alone: the source IP on outbound packets, the destination IP on inbound ones, and the affected IP and transport checksums (RFC 2663 §4.1.1).
- PAT (NAPT) “extends the notion of translation one step further by also translating transport identifier (e.g., TCP and UDP port numbers, ICMP query identifiers)”, which allows “the transport identifiers of a number of private hosts” to be “multiplexed into the transport identifiers of a single external address” (RFC 2663 §4.1.2).
The direction matters. Traditional NAT is built for sessions that start inside — “sessions are uni-directional, outbound from the private network” (RFC 2663 §4.1) — so the reverse path exists only because a mapping was created on the way out.
The mental model: a stateful translation table
INSIDE (private)                  NAT device                    OUTSIDE (public)

 198.51.100.23:51000   ------->   +-------------------+   ---->  203.0.113.7:40001
 (source)                         |  binding table    |        (rewritten source)
                                  |  198.51.100.23    |
                                  |  :51000 -> :40001 |
                                  +-------------------+
                                           ^
 return packet  <--------   lookup destination 40001   <----  203.0.113.7:40001
 198.51.100.23:51000        and rewrite destination

 inbound packet with no matching entry  ->  dropped
Translation runs in three phases — the “creation, maintenance and termination of state for sessions passing through NAT devices” (RFC 2663 §3.2). An outbound packet creates a binding; that binding is what lets the reply be rewritten back to the internal host; when the mapping expires or is removed, the reverse path disappears with it.
The filtering you get, and why it is only a side effect
A packet arriving from outside that matches no entry in the table cannot be mapped onto an internal host, so it is discarded. RFC 5508 states it plainly: “Traditional NAT inherently mandates firewall-like filtering behavior.” But that filtering is a property of the state the translation must keep, not a policy anyone wrote down. RFC 4787 draws the line exactly: the mapping choice “make[s] no difference to the security properties of the NAT. The security properties are fully determined by which packets the NAT allows in and which it does not. This is determined by the filtering behavior.” Translation and filtering are two behaviours; only the second is about security, and that second behaviour is not a firewall.
Why the side effect is not a security control
- It was not designed as one. RFC 4864 says so outright, and notes that a real firewall “often offers explicit and more comprehensive management controls” (RFC 4864 §2.2).
- Static translation forecloses nothing. Where one public address maps to one machine, “the security risk for that machine is identical to the case with no NAT device in the communication path”: any connection to the public address is delivered to the mapped target (RFC 4864 §2.2).
- It can lower security. “NAT (particularly NAPT) actually has the potential to lower overall security because it creates the illusion of a security barrier, but does so without the managed intent of a firewall” (RFC 2993 §9).
- It hides the source you need during a response. Because the internal address is replaced, “the IP address of the host is hidden in a NAT router”, and tracking an abusing host “is more difficult” (RFC 2663 §8.3; RFC 3022 §6.1). Concealment helps an attacker as much as a defender.
- It breaks end-to-end security. NAT devices “break IPsec’s authentication and encryption technologies”, and where NAT is treated as the boundary “the NAT becomes the security endpoint” (RFC 2993 §9).
- Its “rules” are state, not intent. A firewall’s decisions are explicit, reviewable and logged; a NAT’s are whatever the passing traffic created. A mapping opened by malware looks the same to the table as one opened by a browser.
None of this makes NAT useless. It makes the claim false: the mechanism that opens the path is translation, and the protection people attribute to it belongs to a separate, deliberately configured control.
Where translation itself fails
The same limits show the mechanism is not a barrier. Applications that carry an address or port inside their payload need an ALG (Application Level Gateway) to work at all (RFC 2663 §8.1); translation of outbound TCP/UDP fragments in PAT “are doomed to fail” (RFC 3022 §6.3); ICMP error packets need their embedded header rewritten or dropped (RFC 5508); and PAT overloads one address across many hosts, so a single address can run out of ports — the CGN (Carrier-Grade NAT) problem at provider scale (RFC 6888). A control that stops working the moment an application embeds an address is not a control; it is an obstacle to be engineered around.
Level and prerequisites
L3 — operational. The sheet assumes the L1 material on IPv4/IPv6 prefixes and gateways and the L2 sheets of network routing (routing tables, next hop and the default gateway; static routing and default routes). Nothing here is configured: the sheet states what the mechanism is, what each variant rewrites in each direction, and what a reader may and may not claim about it.
Where to go next
Port forwarding as an attack surface, provider-scale carrier-grade NAT and port exhaustion, and stateful firewalls with zoning are later subjects: they belong to other sheets and to Projects. This sheet fixes only the boundary between translation and control.
References
- IETF — IP Network Address Translator (NAT) Terminology and Considerations, RFC 2663 (August 1999) — https://www.rfc-editor.org/rfc/rfc2663 — the definition of NAT and realms (§3, line 324); the private blocks 10/8, 172.16/12, 192.168/16 (line 277); the three phases of translation (lines 409–412); traditional NAT as outbound uni-directional (lines 540–541); Basic NAT (§4.1.1, line 579); NAPT (§4.1.2, lines 593–599); applications with address content needing ALGs (§8.1, lines 1355–1356); the source hidden in a NAT router (§8.3, lines 1396–1397); the “one-way (session) traffic filter” framing (§9, lines 1442–1449).
- IETF — Traditional IP Network Address Translator (Traditional NAT), RFC 3022 (January 2001) — https://www.rfc-editor.org/rfc/rfc3022 — NAT as a privacy mechanism whose side effect makes debugging harder (§6.1, lines 664–681); outbound TCP/UDP fragments in NAPT “doomed to fail” (§6.3, lines 712–715).
- IETF — Network Address Translation (NAT) Behavioral Requirements for Unicast UDP, RFC 4787, BCP 127 (January 2007) — https://www.rfc-editor.org/rfc/rfc4787 — endpoint-independent mapping (REQ-1, line 365); the statement that mapping choice makes no difference to security, which the filtering behaviour determines (lines 358–363).
- IETF — NAT Behavioral Requirements for TCP, RFC 5382, BCP 142 (October 2008) — https://www.rfc-editor.org/rfc/rfc5382 — the security provided by the NAT governed by its filtering behaviour (lines 863–864).
- IETF — NAT Behavioral Requirements for ICMP, RFC 5508, BCP 148 (April 2009) — https://www.rfc-editor.org/rfc/rfc5508 — traditional NAT “inherently mandates firewall-like filtering behavior” (line 139); ICMP error packets matching or dropped against a session (REQ-4, line 679).
- IETF — Common Requirements for Carrier-Grade NATs (CGNs), RFC 6888 (April 2013) — https://www.rfc-editor.org/rfc/rfc6888 — CGN scope and scale; external ports as a shared, limited resource (REQ-4, lines 297–305; “External ports are one of the resources being shared by a CGN”, REQ-13, lines 569–581); endpoint-independent filtering as the default (lines 630–631).
- IETF — Architectural Implications of NAT, RFC 2993 (November 2000) — https://www.rfc-editor.org/rfc/rfc2993 — the illusion of a security barrier lowering overall security (§9, lines 1197–1199); NAT breaking IPsec and becoming the security endpoint (§9, lines 1214, 1269–1271).
- IETF — Local Network Protection for IPv6, RFC 4864 (May 2007) — https://www.rfc-editor.org/rfc/rfc4864 — “IPv4 NAT was not developed as a security mechanism” (line 869); the static-NAT one-to-one case from §2.2 (lines 356–362); the firewall’s “explicit and more comprehensive management controls” (line 375); the PAT port-overload observation (line 344).
- Cisco Systems — IP Addressing: NAT Configuration Guide, Cisco IOS Release 15M&T — the purpose of NAT: private addresses translated to legal ones before forwarding, and advertising one address for the whole network (lines 32–34).